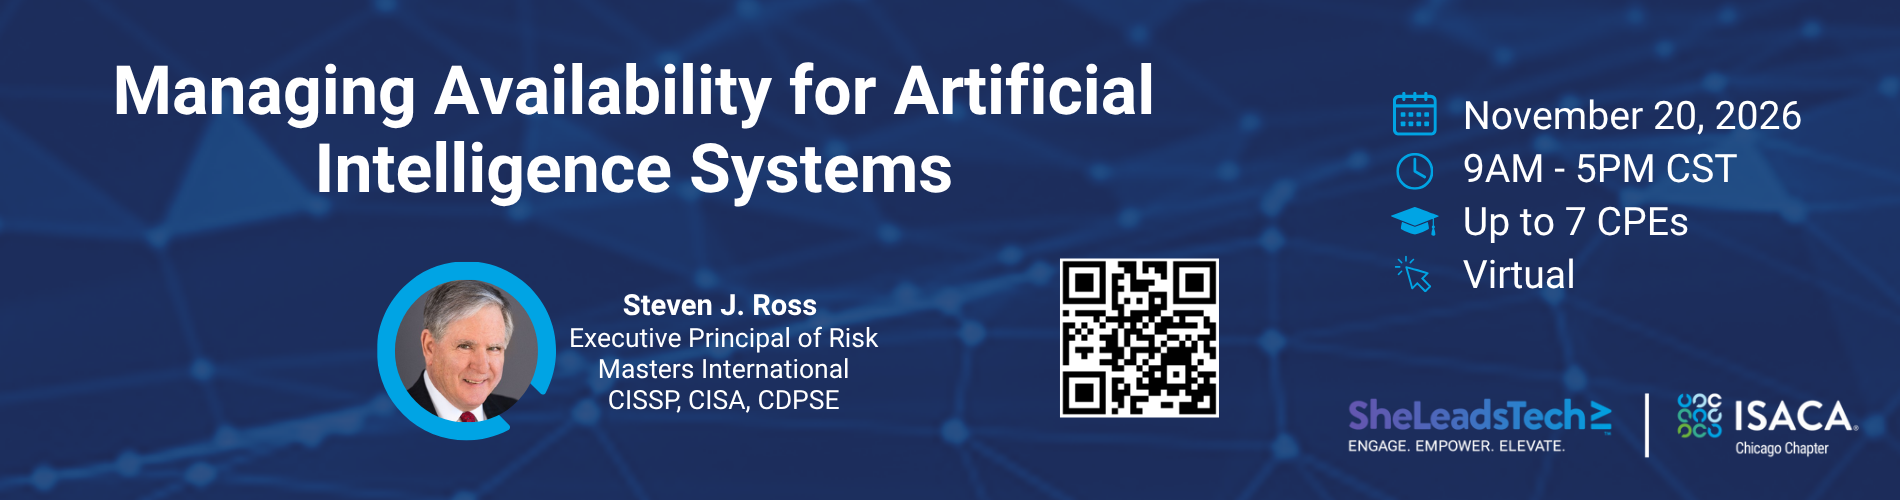
Join us for an immersive one-day virtual workshop designed for Cybersecurity Managers, Internal and External Auditors, Risk Managers, Security Professionals, Business Managers, Financial Executives, and Legal Counsel.
Organizations are placing increasing reliance on artificial intelligence decisions to create products and programs, aid in making important decisions and carrying out routine tasks. The more that businesses rely on AI systems, the greater the need that they be available at all times, under all circumstances. As AI has been introduced into businesses, the immediate concern was how it would be used. Subsequently, the issues of how AI would be controlled, secured and audited came to the fore. It is now timely to determine how AI systems will be made available.
This seminar/workshop explores the requirements for availability, rapidly changing options for achieving it and the organizational and managerial challenges it creates. It draws on current tools and techniques and the experiences of organizations that are successfully meeting the challenge of AI availability.
Learning Objectives: Participants in this seminar will learn:
- Why availability for AI systems is more difficult than for legacy systems
- The business need for AI availability.
- How Enterprise Availability Management is a requirement for AI availability
- What are the current and developing methods for implementing AI availability
- The need for availability standards applicable to AI, and what should be in them
- Governance requirements for AI availability
- Management and technical roles for AI availability
- How AI availability creates career opportunities and challenges
Seminar Outline
- Defining the Problem
- Challenges of AI Availability
- Enterprise Availability Management (EAM)
- AI Availability Solutions
- Implementation Issues
- AI Availability standards and best practices
- Organization and Management for AI Availability
- AI Availability Careers…and Problems
- Conclusion
___________________________________
At a Glance
Date: November 20, 2026
Time: 9 am - 5 pm
CPE: Participants can earn up to 7 CPE Credits in Information Technology.
Delivery Format: Virtual, via Zoom.
**The link to access the virtual event via Zoom will be provided in your registration confirmation email. **
We strongly encourage students to turn on their video cameras during the sessions.
Fees:
*Early Bird Discount: Those who register by November 6, 2026, save $50 off the price of the workshop.
- ISACA Members: $350
- Non-Members: $450
- Students and In-Transition: $150
**There is a 15% discount on registration for groups of six or more for the workshop.
We look forward to seeing you at the Seminar in November 2026!
__________________________________________
Instructor Bio: Steven J. Ross
Mr. Ross is Executive Principal of Risk Masters International and holds certification as a Certified Information Systems Security Professional (CISSP) as well as a Master Business Continuity Professional (MBCP), a Certified Information Systems Auditor (CISA), and a Certified Data Privacy Solutions Engineer (CDPSE). Mr. Ross is a specialist in the field of information systems security and control, specializing in Information Security, Business Continuity Management, Data Privacy, and IT Disaster Recovery Planning services. He has implemented Information Security programs for numerous banks, government agencies, and industrial corporations. Before founding Risk Masters, Mr. Ross was a Director and global practice leader with Deloitte & Touche.
In consulting engagements, he specializes in planning, policy development, implementation, and standardization of Information Security processes. In recent years, his focus has been on reliability, prevention, detection and recovery from the technical and business impact of cyberattacks. He has published a book, Creating a Culture of Security. He was editor of the multi-volume series, e-Commerce Security, and author of several of the books in the series, including e-Commerce Security: Public Key Infrastructure. Since 1998, Mr. Ross has regularly published the column, “IS Security Matters”, in the ISACA Journal. In 2022, he was inducted into the ISACA Hall of Fame.