Following the Annual General Meeting, ISACA Sweden welcomes members and guests to the Spring Conference 2026, an afternoon dedicated to current developments in governance, risk, privacy, AI, and cybersecurity.
The 2026 program brings together experienced practitioners and international experts who will address practical and strategic challenges facing organisations across sectors. The sessions focus on measurable capability, regulatory expectations, and the evolving relationship between technology, risk, and trust.
Registration opens on the 20th of February
Preliminary Agenda
If you are a member and want to sign up for the entire event, including the AGM, please click here
| Time |
Agenda item |
| 11.30 |
Registrering inför årsstämma
Registration for AGM |
| 11.45 - 12.15 |
Årsstämma börjar enlig separat anmälan och röstlängd
AGM |
| 12.15 - 12.45 |
Enkel lunch för deltagare på årsstämman
Simple lunch for AGM Participants |
| 12.45 - 13.00 |
Registration + Coffee & Tea / Registrering vårkonferens + kaffe & te |
| 13.00 - 13.05 |
Moderator John Wallhof öppnar dagen
Opening by John Wallhof |
| 13.05 - 14:00 |
Session 1 - Jörgen Holmlund - Vem gör du egentligen affärer med – hur jobbar utländska stater och organiserad brottslighet med att uppträda i bolag |
| 14.00 - 14.25 |
Fika |
| 14.25 - 15.20 |
Session 2 - Ulrika Dellrud - Privacy in the Age of AI: From Compliance to Trust |
| 15.20 - 15.45 |
Fika |
| 15.45 - 16.40 |
Session 3 - Robert Willborg - Risk på riktigt: från sårbarhet till bevisbar förmåga |
| 16.40 - 17.00 |
Wrap-Up / Closure / Summering / Frågor |
| 17.00 - 18.00 |
Mingle/Reception |
Fees
For members, signed via the Annual General Meeting with confirmed attendance at Spring Conference, do not need to register separately.
For members and non-members only attending the conference, a fee of 500 SEK (excl. VAT) - Non-refundable - will be charged and can only be payed using payment card. No-show without previous notification is charged 500 SEK (excl. VAT)
Attendance is not confirmed until payment has been received.
Last day to sign-up is on 6th of April and last day to cancel is 14th April.
Sessions
Robert Willborg
Risk på riktigt: från sårbarhet till bevisbar förmåga
Session in Swedish
This session examines risk from an operational perspective. Moving beyond policy documentation and theoretical matrices, the focus is on vulnerability, exposure, and consequence in real organisational contexts.
Key questions addressed include:
• What can be stopped within hours?
• What can be detected within minutes?
• How does an organisation maintain operational continuity over days?
The session reflects the increasing emphasis on demonstrable capability in light of evolving regulatory and threat landscapes, including NIS2.
Ulrika Dellrud
Privacy in the Age of AI: From Compliance to Trust
Session in English
Artificial intelligence introduces new categories of privacy risk that extend beyond traditional compliance and security frameworks. This session explores how privacy and ethics must be embedded directly into AI governance to ensure accountability, resilience, and public trust.
Topics include:
• Emerging privacy risks introduced by AI systems
• The evolving EU regulatory landscape, including the AI Act and its interaction with GDPR
• Strengthening data governance and accountability mechanisms
• Moving beyond compliance toward trust as a strategic advantage
Jörgen Holmlund
Vem gör du egentligen affärer med – hur jobbar utländska stater och organiserad brottslighet med att uppträda i bolag
Session in Swedish
Topics include:
• How foreign states and organised crime use companies as tools for influence, intelligence gathering and economic gain
• How legitimate corporate structures can be used to hide real ownership and strategic interests
• Methods used to gain influence in strategic sectors, investments and supply chains
• Real-world examples from international security and intelligence environments
• Warning signs organisations should watch for in partnerships, suppliers and investments
• How companies can strengthen their ability to identify and manage these risks in an increasingly complex geopolitical landscape
The full agenda and detailed session topics will be published in the coming weeks.
Speaker Bio's
Jörgen Holmlund is a former Senior Superintendent of Police and one of Sweden’s most experienced security experts. He has held senior roles within the Swedish Police and the Swedish Armed Forces, including international deployments, and contributed to the development of the United Nations Military Intelligence Handbook.
From 2008 to 2010, he led the Swedish Police International Operations Unit, overseeing peacekeeping deployments in cooperation with the EU, UN and OSCE. He is an Adjunct Professor of Law Enforcement Intelligence at Mercyhurst University, USA, and lectures in Strategic Intelligence at the Swedish Defence University, where he is also engaged in Financial Intelligence education.
Jörgen serves as a strategic advisor, supporting organisations in strengthening security governance, intelligence capabilities and international cooperation.
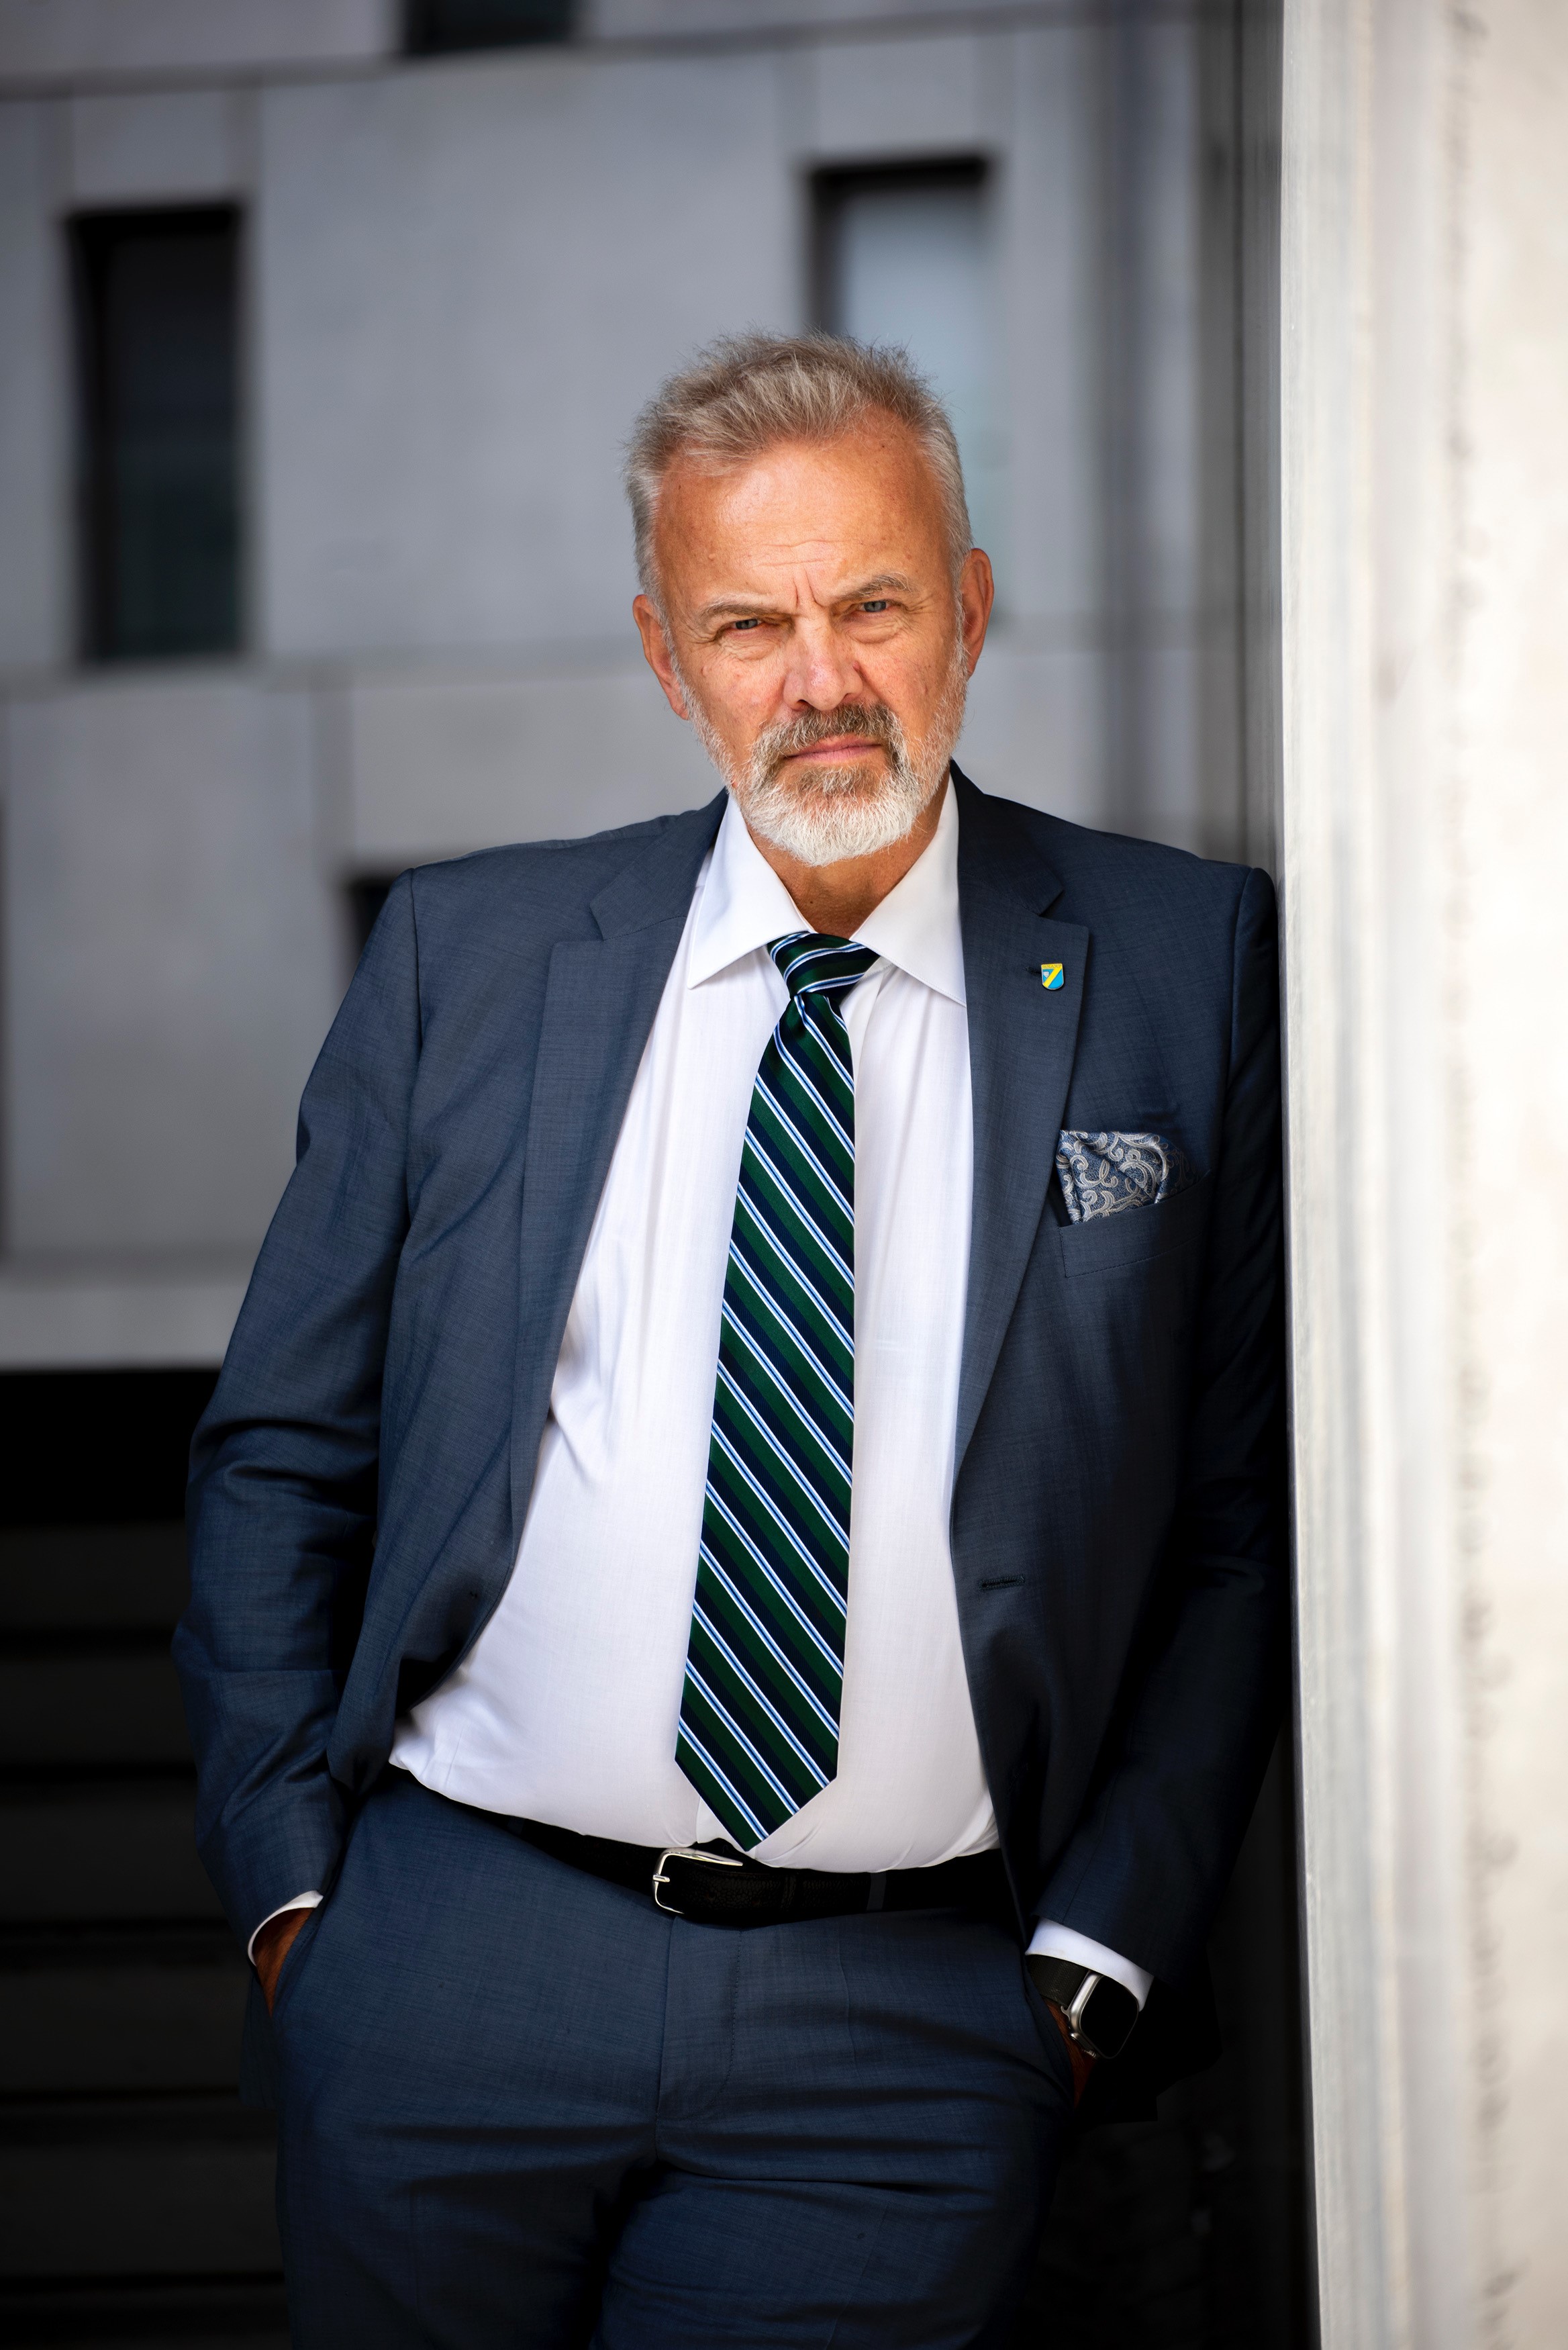
Robert Willborg is a cybersecurity expert known for making risk tangible, concrete and impossible to ignore. Operating at the intersection of real-world supply chain security, provable resilience and human behaviour, he challenges organisations to move beyond compliance theatre toward measurable, auditable and operational security that works under pressure.
He is the founder of the OMS Declaration and creator of the STAR Model, Risk Model 2.0 and Risk Model 2.1, frameworks focused on reducing documentation overload and building security that actually stops, detects and enables organisations to survive incidents across internal environments and entire supplier ecosystems.
A recognised security evangelist in cyber psychology, cyber hygiene and practical cybersecurity, Robert combines strategic oversight with a relentless focus on impact. As an international speaker, most recently in France and Finland, he urges leaders to build demonstrable capability in line with evolving EU requirements such as NIS2, without turning risk reduction into a paper exercise.
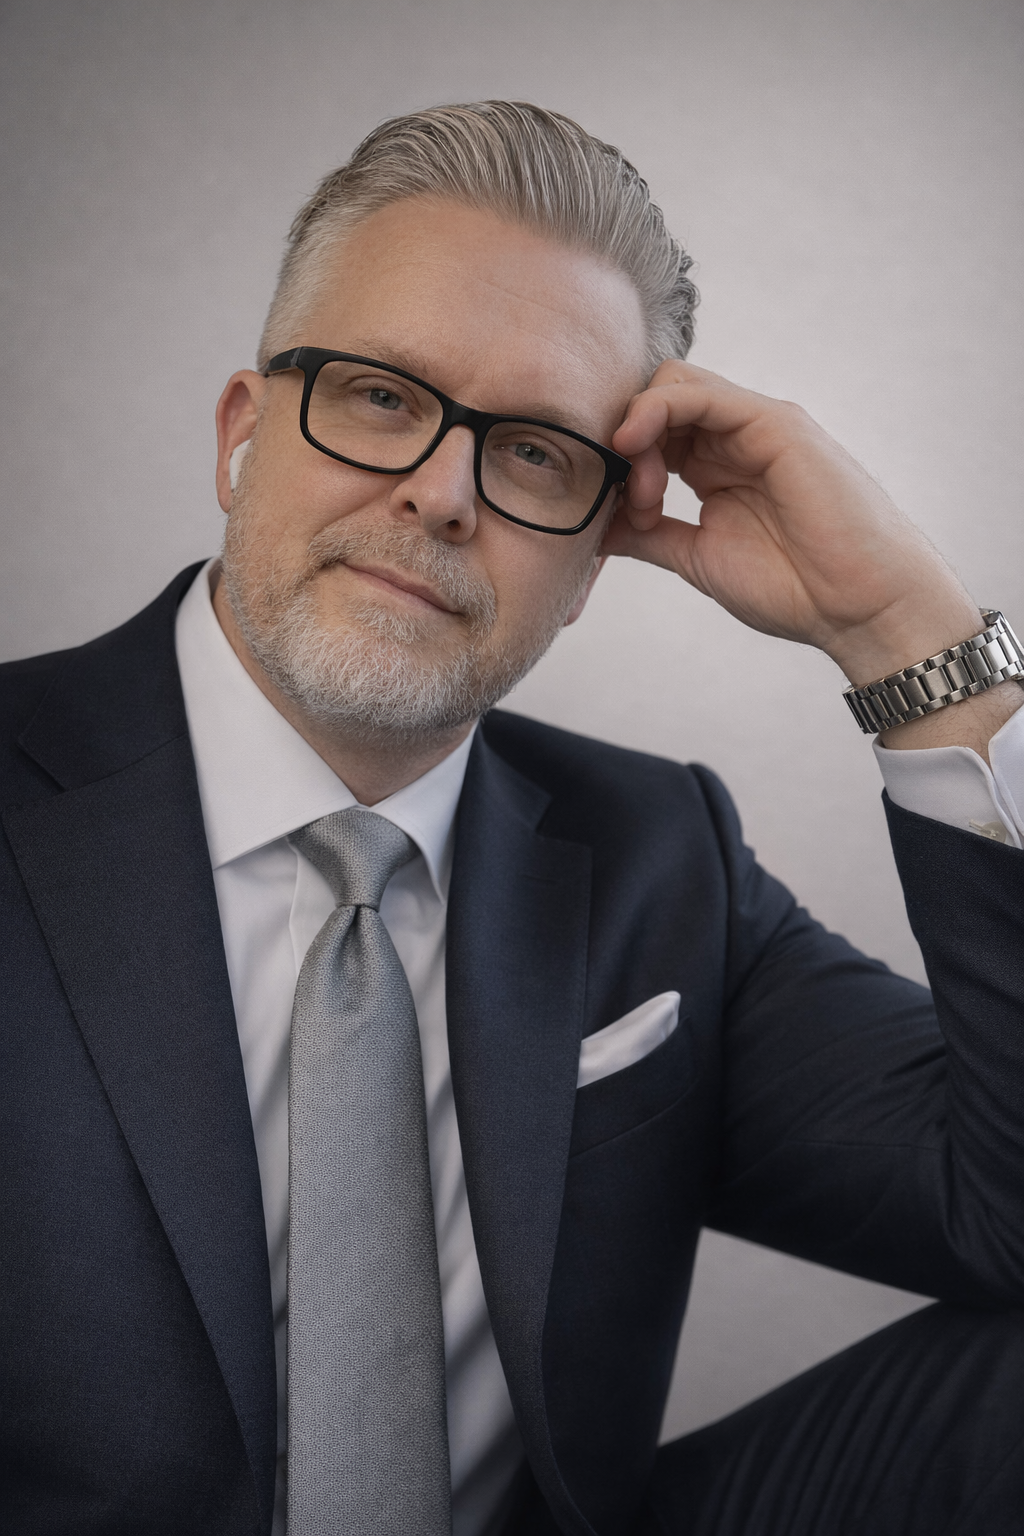
Ulrika is a globally recognised leader in privacy, data, AI and digital ethics, with more than 25 years of strategic and operational experience. She has served as EMEA and Global Chief Privacy Officer for major multinationals. She is currently the Chief Privacy and Data Ethics Officer at Smarter Contracts and a Non-Executive Director, advising companies on governance and responsible innovation.
She actively engages with global regulators, advises the European Data Protection Board, and serves on the IAPP AI Governance Board. A dual-qualified Swedish and US attorney and member of the New York Bar, she received the inaugural IAPP Hughes Leaders Award in 2022.
Ulrika is a former board member and Certification Director at ISACA Belgium, a dedicated mentor and strong advocate for women in privacy and technology. Amongst others, she has the following certifications under her belt: CIPP/E, CIPM, FIP, AIGP, NYBA

Moderator
Our trusted moderator is John Wallhoff, an experienced board advisor and cybersecurity professional with a long background in IT governance and audit. As a former President of ISACA Sweden and a seasoned CISA and CISM, John brings both strategic boardroom insight and operational depth.
For the past few years, he has skillfully moderated our sessions, connecting themes, challenging perspectives and keeping both speakers and audience constructively on their toes.