ISACA Sweden Chapter is pleased to announce that ISACA Dagen 2026 will take place on 16 November 2026.
As in previous years, ISACA Dagen will bring together professionals and leaders from across cybersecurity, information security, governance, risk, audit, privacy, resilience, compliance and digital trust for a full day of insights, discussion, practical experience and networking.
This year's programme is now taking shape, and over this week and next week we will begin revealing the speakers and sessions that will make up ISACA Dagen 2026.
Rather than publishing everything at once, we will introduce our speakers one by one, together with more information about their background and the topics they will bring to the stage. The complete programme and agenda will be published as these announcements are released.
Topics will span the ISACA domains and some of the most important challenges currently facing our profession, including security, governance, risk management, audit and assurance, privacy, resilience, regulation, AI governance, emerging technology and digital trust.
ISACA Dagen is also an opportunity to meet colleagues from across the community and exchange experiences with security professionals, auditors, risk and compliance specialists, technology leaders, consultants, students and other professionals working within the ISACA domains.
Preliminary Agenda
Please note that the programme and exact session times are preliminary and may be adjusted. They are currently added in slot order of speaker announcement
| Time |
Programme |
| 08:30 - 09:00 |
Registration, Coffee & Networking |
| 09:00 - 09:10 |
Welcome to ISACA Dagen 2026 with John Wallhoff |
| - |
Bjørn R. Watne, Global CISO, INTERPOL Succeeding with Security at Scale: Lessons Learned from a Career Across Borders and Communities |
| - |
Coffee Break & Networking |
| - |
Pia Gruvö, Cryptography Strategist at MUST Krypto för skydd av det mest skyddsvärda, kvantdatorers påverkan samt något om en nyckel till internet. (Swedish) |
| - |
Fredrik Olsson Populärvetenskaplig presentation av grundforskning inom riskhantering. Vad forskas det på och varför då? (Swedish) |
| 12:05 - 13:05 |
Lunch & Networking |
| - |
Session 4 - Speaker announcement coming soon |
| - |
Coffee Break & Networking |
| - |
Session 5 - Speaker announcement coming soon |
| - |
Coffee Break |
| - |
Closing Session / Discussion |
| 16:50 - 17:00 |
Wrap-up and Closing Remarks |
| 17:00 |
Reception |
| - |
Dinner (Optional fee) |
Additional speakers and session titles will be announced continuously as we approach the event.
Your Moderator for the Day
We are delighted to once again welcome John Wallhoff as moderator and host of ISACA Dagen.
John is an experienced board advisor and cybersecurity professional with a long background in IT governance, audit and information security. A former President of ISACA Sweden and a seasoned CISA and CISM, John combines strategic boardroom insight with extensive operational experience.
John has become a familiar face at our conferences over the past few years, skilfully connecting the themes of the day, challenging speakers and perspectives, engaging the audience and making sure that discussions continue beyond the individual presentations.
We are very happy to have him back to guide us through ISACA Dagen 2026.
Registration is open
The registration flow for ISACA Dagen 2026 is open!
Further information about the venue, speakers, programme, agenda and practical arrangements will be published shortly.
Important dates
- Registration: Open now
- Official launch and Early Bird: 1 September 2026
- Programme and speaker announcements: Starting this week
- ISACA Dagen 2026: 16 November 2026
We look forward to welcoming you to another inspiring ISACA Dagen and to bringing the ISACA Sweden community together once again on 16 November 2026.
Speaker Bio and Session Details
Bjørn R. Watne
Chief Information Security Officer, INTERPOL
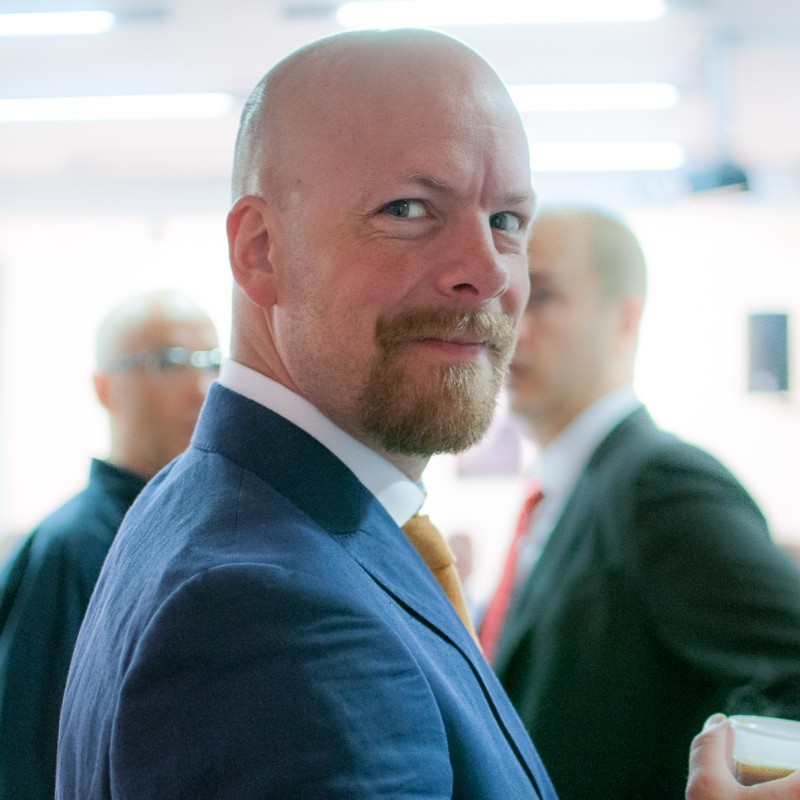
Succeeding with Security at Scale
Lessons learned from a career across borders and communities
“If you want to go far, go together.”
Cybersecurity does not stop at organizational or national borders. Neither can effective security leadership.
Drawing on 25 years of experience across Europe and Asia, Bjørn R. Watne will share lessons from a career spanning critical infrastructure, telecommunications, financial services and international law enforcement.
As Global CISO at INTERPOL, Bjørn leads the organization’s cybersecurity vision and defensive posture in an increasingly complex and borderless threat landscape. He previously served as SVP and Chief Security Officer at Telenor Group and Group CISO at Storebrand/SPP.
His session brings together three perspectives:
- A cybersecurity practitioner working across countries and industries
- An ISACA leader building professional communities and networks
- An international organization addressing transnational security challenges
The central message is simple: security at scale requires collaboration, shared purpose and the ability to turn professional communities into practical resilience.
Bjørn is a long-standing member of the ISACA community and served as President of the ISACA Norway Chapter for more than a decade. He holds an Executive MBA from ESCP Business School and certifications including CISA, CISM, CRISC, CGEIT, CDPSE and CISSP-ISSMP.
Pia Gruvö
Cryptography Strategist, Swedish Military Intelligence and Security Service (MUST)
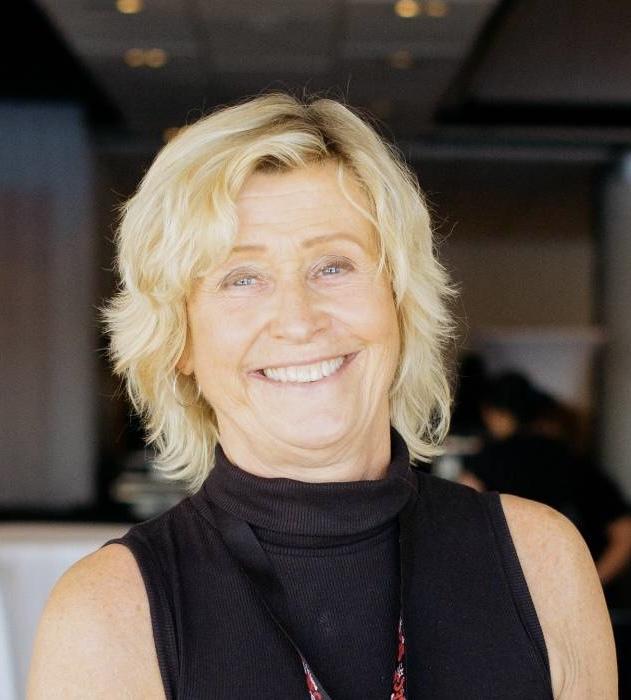
Krypto för skydd av det mest skyddsvärda, kvantdatorers påverkan samt något om en nyckel till internet. (Talk in Swedish)
Few people work as closely with both Sweden’s most sensitive information and the cryptographic foundations of the global internet as Pia Gruvö.
Pia serves as a Cryptography Strategist at the Swedish Military Intelligence and Security Service (MUST). She has nearly 40 years of experience working with cryptographic systems designed to protect information requiring the highest levels of security.
Since 2022, Pia has also served as a Crypto Officer for ICANN and IANA. She is one of only 14 people worldwide entrusted with what is commonly known as a “key to the internet”.
In this role, Pia participates in rigorously controlled and publicly audited ceremonies that safeguard DNSSEC and the DNS root. In 2024, she helped generate KSK‑2024, the new root signing key at the centre of the 2026 DNSSEC key rollover.
Pia brings a rare perspective spanning national security, long-term cryptographic strategy and the operational trust mechanisms underpinning global digital infrastructure.
Fredrik Olsson
Risk Researcher, KTH Royal Institute of Technology
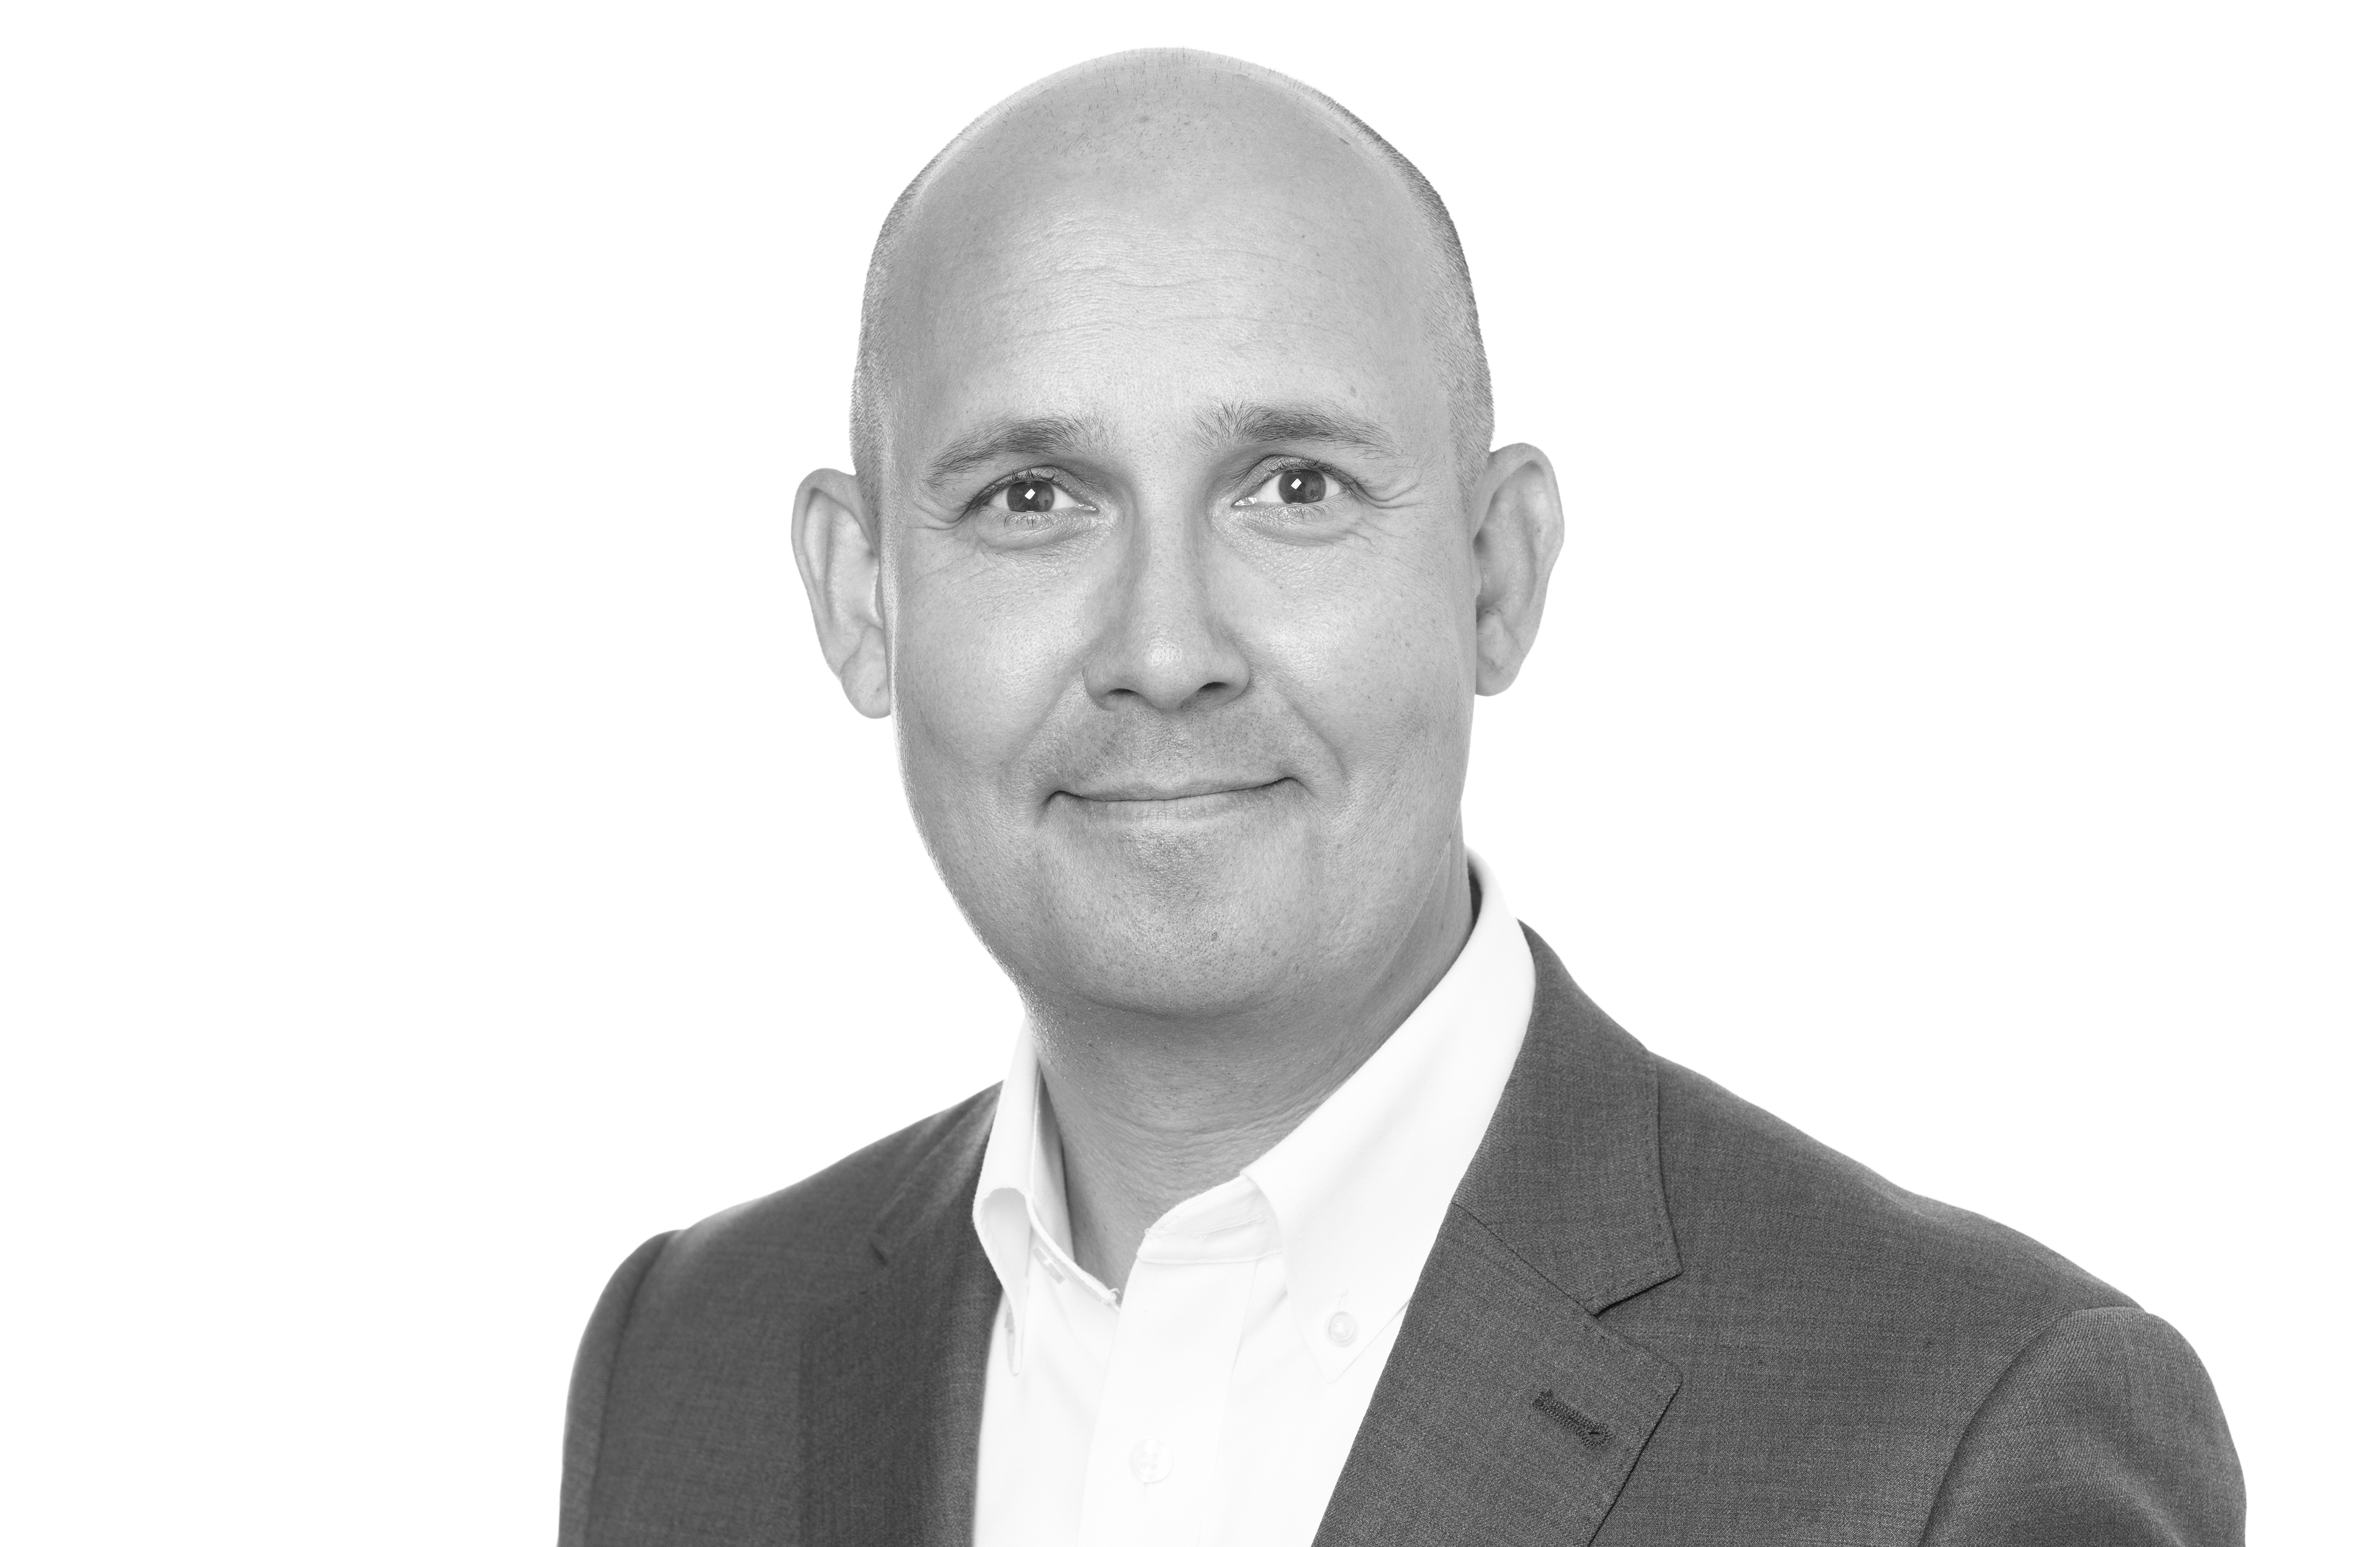
Populärvetenskaplig presentation av grundforskning inom riskhantering. Vad forskas det på och varför då? (Talk in Swedish)
How do we understand risk, what makes our knowledge reliable, and how do we make decisions when uncertainty cannot be resolved?
Fredrik Olsson researches risk at the intersection of philosophy and decision theory at KTH. He brings more than 25 years of experience in risk management, primarily within banking and financial services, connecting fundamental research with the decisions organizations face in practice.
His background includes positions as Chief Risk Officer (CRO) and head of operational risk, alongside experience establishing risk functions, advising financial institutions and serving on boards. He is also a frequent lecturer on risk.
At ISACA Dagen, Fredrik will offer an accessible introduction to risk science, exploring what researchers are studying and why it matters for professionals working with governance, risk, security and assurance.
His session will explore:
-
Risk and uncertainty: how we understand risk and how statistical approaches influence our decisions.
-
Reliable risk knowledge: how we develop sound foundations for assessments and recognize the limitations of our methods.
-
Judgement, values and ethics: how subjective perspectives shape risk assessments and decisions under uncertainty.
By bringing research and professional experience together, Fredrik invites participants to examine the assumptions behind familiar risk practices and broaden their understanding of how risk can be assessed and managed.